
ThreatMirror at GovWare and SWITCH 2026
October was an exciting month for the OverArX team as we participated in two major technology exhibitions in Singapore: GovWare 2026 and Singapore Week of Innovation and Technology (SWITCH) 2026.
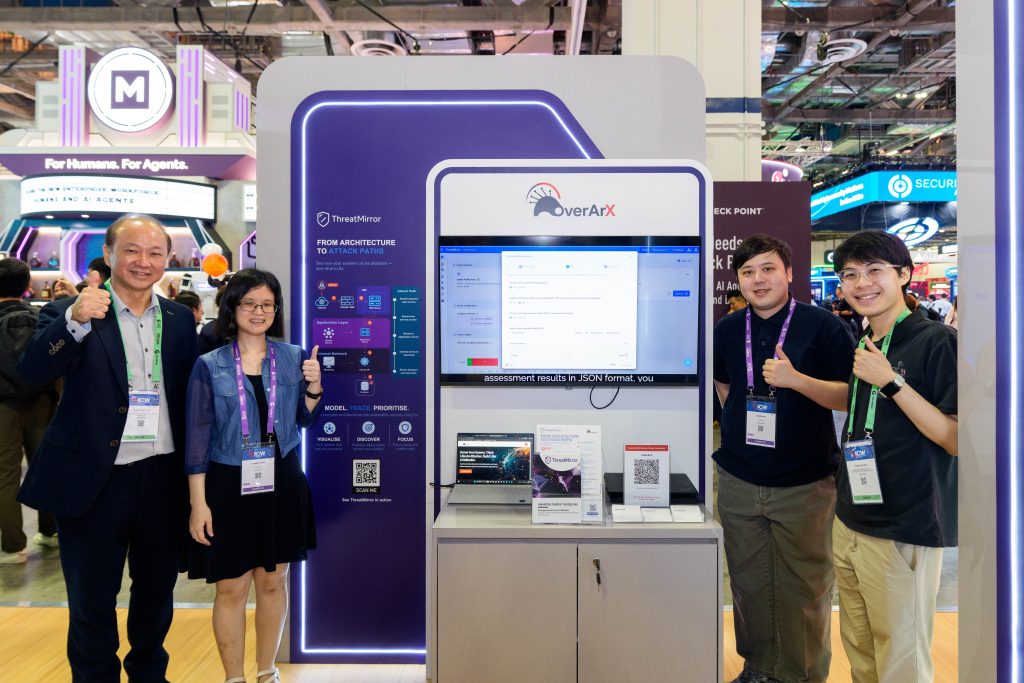
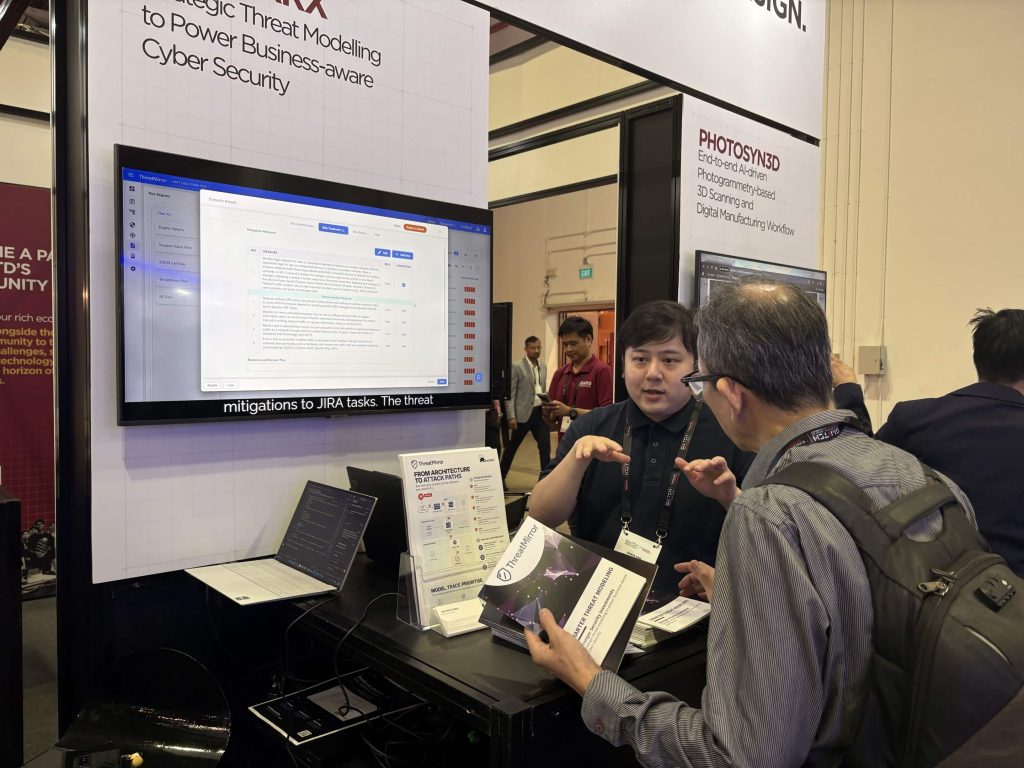
Across both events, we showcased ThreatMirror through a healthcare use case involving interconnected medical devices and supporting infrastructure. The demonstration illustrated how ThreatMirror analyses system architectures and data flows to identify potential attack paths, highlight critical weaknesses and recommend actionable countermeasures.
Connecting with the industry
At GovWare, we had the opportunity to introduce ThreatMirror to cybersecurity professionals and industry practitioners, sharing how an attack-path-based approach can help organisations better understand their security risks.
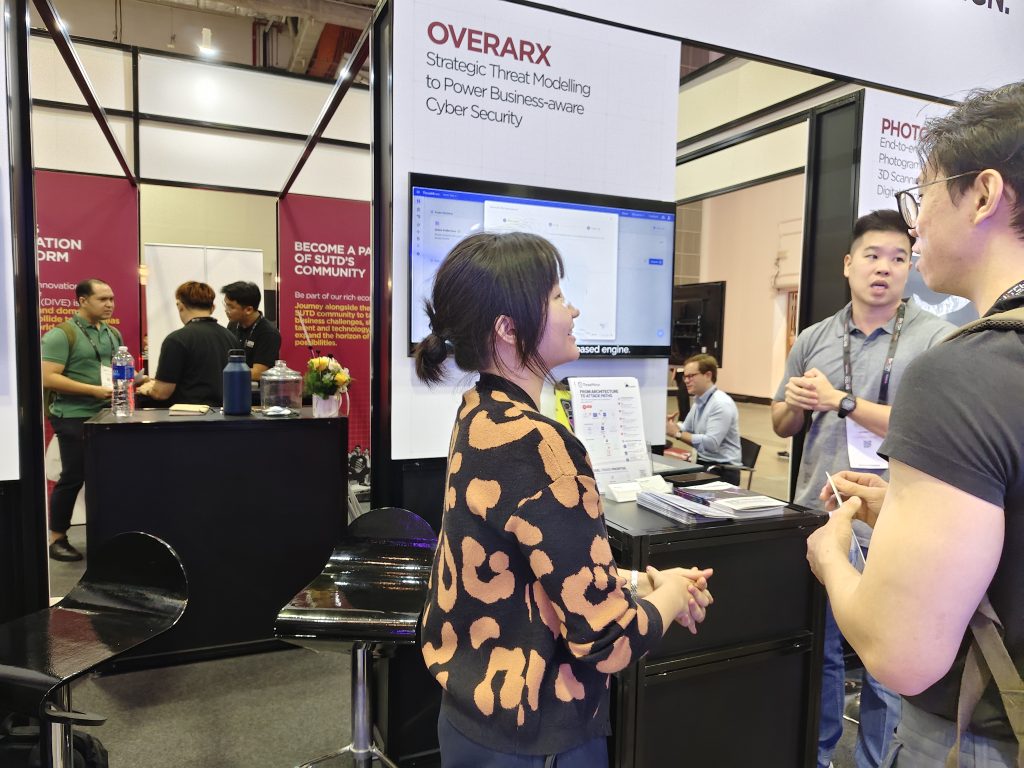
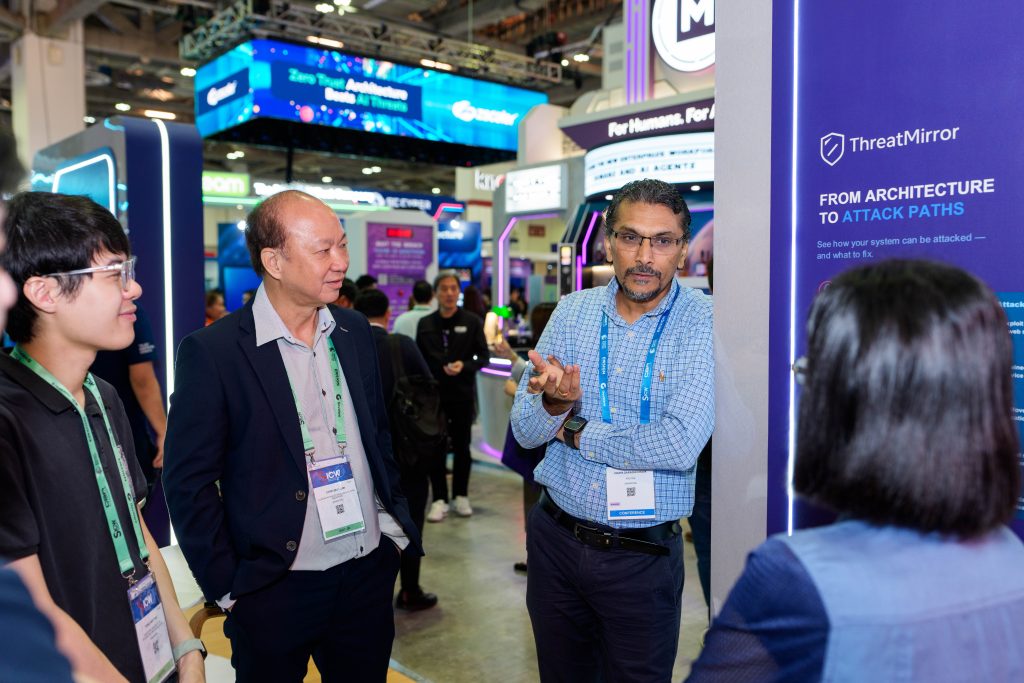
At SWITCH, we brought the same demonstration to a broader technology and innovation audience. We also connected with potential collaborators, including managed service providers (MSPs) and compliance-focused service providers, and met smaller organisations and law firms interested in exploring ThreatMirror through trial accounts.
What we learned
One particularly encouraging takeaway from both exhibitions was the recognition that organisations need more than extensive lists of vulnerabilities. They need to understand which weaknesses are most important to address and how these could be exploited together.
This is exactly what ThreatMirror aims to achieve: helping organisations move beyond identifying individual vulnerabilities towards understanding potential attack scenarios and prioritising the security measures that matter most.
The conversations also highlighted opportunities to bring threat modelling to a wider range of organisations, including those without dedicated cybersecurity teams.
Looking ahead
Participating in GovWare and SWITCH was an important opportunity to showcase our work, gather industry perspectives and explore potential collaborations.
We look forward to following up on these conversations, welcoming organisations interested in trying ThreatMirror, and continuing to make proactive cybersecurity more accessible and actionable.
A big thank you to everyone who visited us, watched our demonstrations and shared their insights. We look forward to connecting again!
Stay tuned for more updates from the ThreatMirror team.